Course: Software Security (KOSEN69) · Covers: Weeks 1–6 Time: 120 min · Total: 100 pts · Closed book unless stated otherwise.
Name: ____________________ Student ID: ____________ Date: ________
Answer in your own words. For code answers, write the exact payload/fix. Sandbox/ethics rules apply to all scenarios.
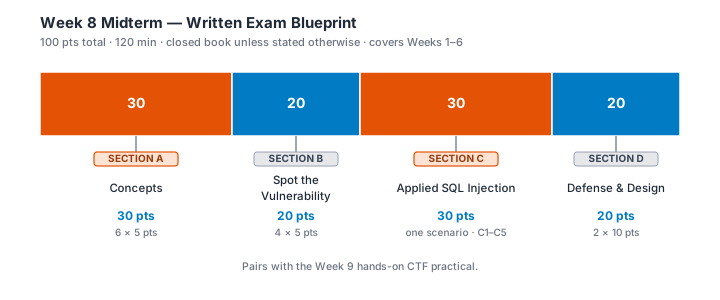
Section A — Concepts (30 pts, 5 each)
A1. Define the CIA triad and give one realistic threat against each property.
A2. Map each STRIDE letter to the security property it violates.
A3. Compare SAST vs DAST vs SCA vs fuzzing — what each sees and when it runs.
A4. Explain hashing vs encryption vs encoding, with one correct use of each.
A5. What is a trust boundary? Identify two in a typical web app + database.
A6. Define least privilege and fail closed, with one example each.
Section B — Spot the Vulnerability (20 pts, 5 each)
Name the vulnerability (+ CWE) and give the fix.
B1.
q = "SELECT * FROM users WHERE name='" + request.args["name"] + "'"
db.execute(q)
B2.
return f"<h1>Hello {request.args['name']}</h1>" # rendered in the browserB3.
data = jwt.decode(tok, options={"verify_signature": False})
if data["role"] == "admin": grant()
B4.
import hashlib
def store(pw): return hashlib.md5(pw.encode()).hexdigest()
Section C — Applied SQL Injection (30 pts)
A login runs this query (both fields are required, cannot be blank):
SELECT uid, name, salary, password FROM usertable
WHERE profileID = 10 AND password = '<hash>'
C1. (6) profileID is an integer parameter. What do you put in profileID and password to log in without the password? Explain why it works.
C2. (6) Now profileID is a string (WHERE profileID='10' AND password='...'). Give the injection and explain the difference from C1.
C3. (6) The form is submitted via GET: /login?profileID=a&password=a. Write the edited GET request to bypass auth, and explain the comment handling.
C4. (6) You can inject into an UPDATE on an edit-profile page. Write three different injections to fingerprint whether the DB is MySQL/MSSQL, Oracle, or SQLite (version).
C5. (6) Write a subquery to dump all table names from a SQLite DB into one field. (Hint: group_concat + sqlite_master.)
Section D — Defense & Design (20 pts, 10 each)
D1. List three distinct defenses against SQL injection and explain why client-side validation is not one of them.
D2. You must add a "reset password" feature. Describe a secure design: token generation, storage, expiry, and how you avoid IDOR and account enumeration.
End of exam. Pair with the Week 9 hands-on CTF practical.